How to Show Used Ports in Linux (ss, netstat, lsof)
Show used (open) ports in Linux with ss, netstat and lsof. Quick commands to list listening ports, find which process uses a port and filter by TCP/UDP.
Every web address ends up at a port number. HTTP reaches the server on port 80, HTTPS on port 443. Both numbers are registered with IANA, which is why they mean the same thing on every machine.
The question only gets interesting once two services want the same port. A web server such as NGINX or Apache then refuses to start and reports that the address is already in use. It does not say who took it.
I run my own servers on NGINX because it works as a web server and a reverse proxy at the same time. It accepts the request on port 443 and hands it on internally — to an Apache, to another domain, or to a Docker container listening on 8080 or 8443. Convenient, yes. It also means a single machine ends up holding a dozen ports, and after a few months nobody remembers which service owns which one.
Three tools answer that question: lsof, netstat and ss. They ship in three different packages. Each takes a different route to the same answer.
Checking open ports with lsof
On Debian and Ubuntu, lsof is not part of the base install. A lean server image usually goes without it. Install it first:
sudo apt install lsof -yThe name is short for list open files, and that is exactly the job: it reports which process has which file open. On Linux a network socket counts as a file too, which is how the tool ends up listing open ports as a side effect. The call takes four parts:
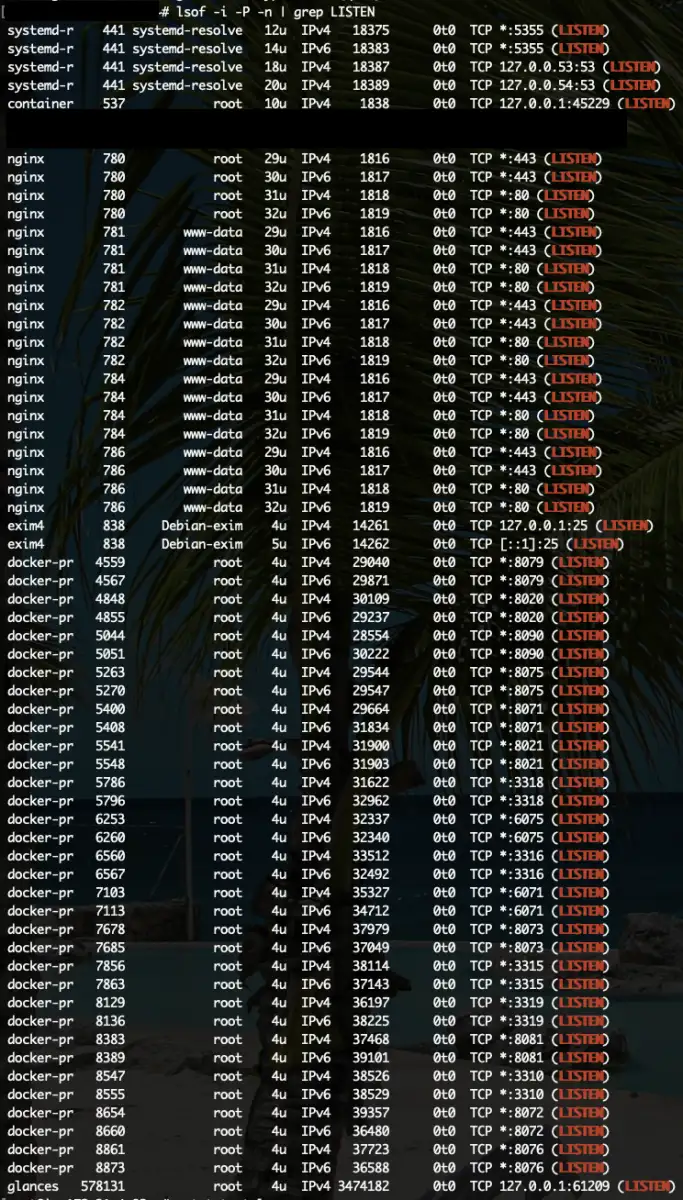
sudo lsof -i -P -n | grep LISTENYou get one line per connection that is sitting on the system waiting for requests. What the options do:
- -i: limits the output to network connections instead of every open file.
- -P: keeps port numbers as numbers rather than turning 22 into ssh and 443 into https.
- -n: skips name resolution for addresses. On a host with slow DNS this alone saves several seconds per call.
- grep LISTEN: drops the established connections and keeps the listening ones.
The first column gives the process name. The second gives its PID. That already answers the real question: which port is taken, and by what. One catch. Without sudo you only see your own processes, and the services worth looking at usually run as root or under a user of their own.
Listing ports with netstat
netstat lives in the net-tools package, and on current systems that package is often absent. Ubuntu 22.04 LTS ships without it, while ss sits at /usr/bin/ss from the start. If you want netstat anyway:
sudo apt install net-tools -ynetstat prints routing tables, interface statistics and, of course, the ports in use. It is the command most tutorials still reach for. Its own manual page disagrees and opens with the line “This program is mostly obsolete. Replacement for netstat is ss.” It still does the job:
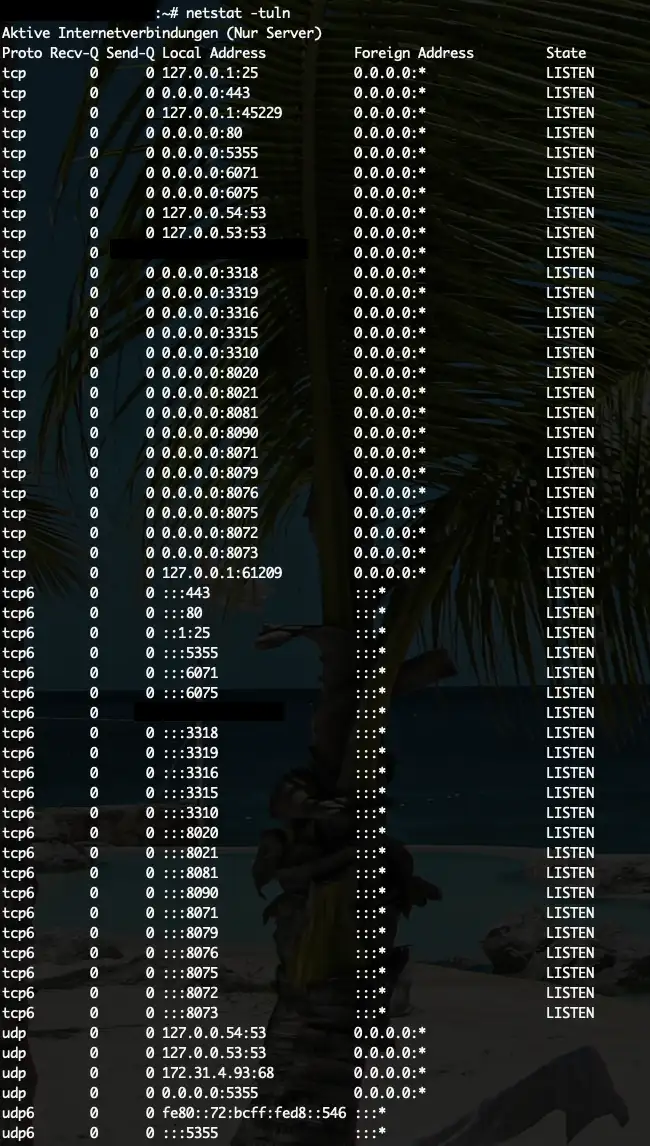
netstat -tulnThe four letters select TCP (-t), UDP (-u), listening sockets only (-l) and numeric output without name resolution (-n). Add -p and the last column names the PID and the process holding the port — that variant needs sudo.
Listing ports with ss
ss comes from the iproute2 package. Debian and Ubuntu give that package the priority important, so it is there on virtually every install, minimal container images included. You will rarely need the next line — only if the package really is missing:
sudo apt install iproute2 -yThe name stands for socket statistics. Its manual page sums the tool up in two sentences: it shows information similar to netstat, and it can display more TCP and state information than other tools. The claim that ss is also faster turns up in plenty of tutorials but not in the manual page — and on a box with a few dozen sockets you would not notice either way. The call mirrors netstat:
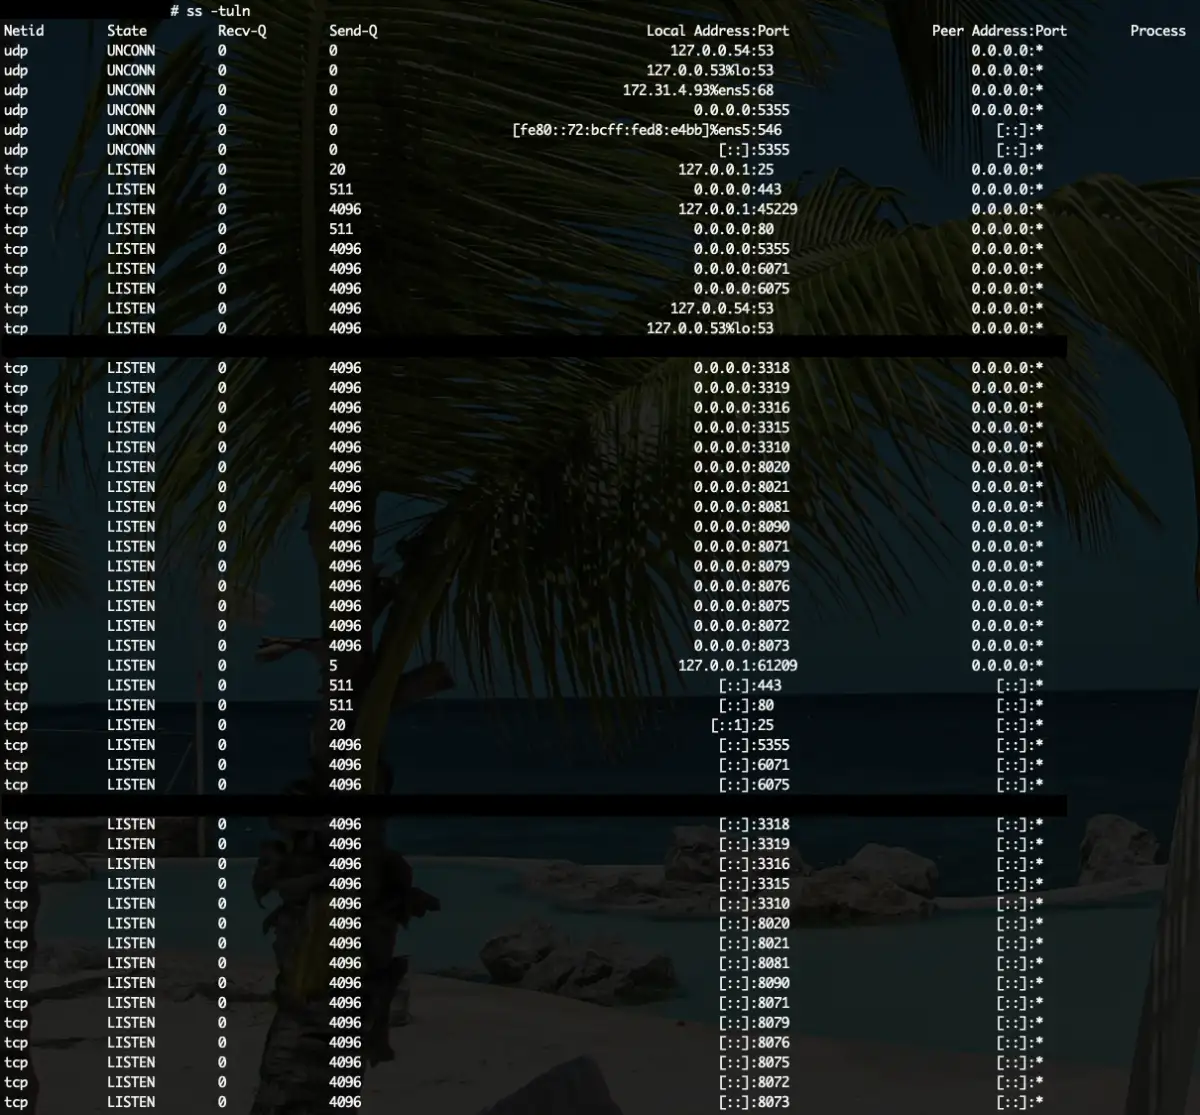
ss -tulnThe output lists the same TCP and UDP ports in a slightly different shape. The variant worth remembering carries an extra p: ss -tulnp puts the owning process at the end of every line. That is the call you want. Knowing that port 8080 is busy gets you nowhere; the PID behind it does.
Which one to reach for comes down to three lines. ss -tulnp first, because the package is on every system. lsof when the question starts from the file side — a process is holding a directory and you want to know what else it has open. And netstat only when you are on an older machine where ss genuinely is not installed.